

Telehealth promised to make healthcare feel human again: no more sitting on hold, no more waiting rooms, no more racing to squeeze a doctor’s appointment into a lunch break. You open an app, answer a few questions, and within minutes a prescription is on its way to your pharmacy. That convenience exploded after the pandemic, as dozens of online health companies began offering quick access to medications for ADHD, anxiety, sexual dysfunction, weight loss, and more. For millions of people, especially those with busy schedules or limited access to primary care, these services felt like a lifeline. But beneath the smooth interface and reassuring marketing, a troubling pattern has emerged. Government regulators are increasingly accusing some of the most popular telehealth companies of practices that feel more like a shady subscription trap than a medical office: sharing sensitive health data with advertisers, enrolling customers in recurring charges that are hard to cancel, and approving prescriptions without any real conversation with a doctor. The very convenience that made these platforms so appealing is now at the center of a growing fight over consumer protection, privacy, and what we should expect from healthcare in the digital age.
The Federal Trade Commission has taken aim at several major telehealth providers in recent years, and its latest lawsuit targets Hims & Hers, one of the best-known names in the industry. The FTC alleges that the company engaged in deceptive and unethical practices, including disclosing customers’ health information to Meta and other online platforms without permission, automatically enrolling users in subscription programs with little opportunity to review the provider’s recommended treatment, and bypassing real-time consultations with clinicians. Hims has pushed back, calling the government’s claims “an effort to generate headlines at our expense.” But the company is not alone. The FTC has filed similar cases against online therapy provider BetterHelp and pharmacy discount service GoodRx, both of which were accused of sharing users’ health data with companies like Google and Meta after promising to keep that information private. These are not fly-by-night operations; they are platforms that millions of people have trusted with some of the most personal details of their lives. The fact that regulators keep finding the same troubling behavior across different companies suggests a systemic problem, not just a few bad actors. And yet, the legal tools available to protect consumers are surprisingly weak, leaving many people exposed in ways they never imagined.
Part of the problem is that many telehealth companies operate in a gray area when it comes to privacy law. Most Americans assume that any health information they share with a medical provider is protected by HIPAA, the federal law that sets strict rules for how doctors, hospitals, and insurers handle medical records. But HIPAA does not generally apply to direct-to-consumer telehealth companies, even those that prescribe medication, offer counseling, or sell DNA tests. That means the sensitive details you type into an online questionnaire about your mental health, your weight struggles, or your sexual function may not be covered by the same legal protections you would expect from a traditional doctor’s office. According to Andrew Crawford, an attorney with the Center for Democracy and Technology, there is “an entire universe of companies collecting huge amounts of consumer health data every day that aren’t covered by our current health sector-specific laws.” The result is a legal landscape where companies are not explicitly forbidden from sharing health data with advertisers, and enforcement often happens only after the damage is already done. The FTC has tried to step in using its broader authority against deceptive practices, but that approach requires proving that a company said one thing and did another, a slow and limited process. Meanwhile, consumers are left to assume that their private health information is safe, when in reality it may be flowing to data brokers, ad networks, and social media platforms.
What does a typical telehealth visit actually look like? For most people, it does not involve seeing a doctor face-to-face, or even over video. Instead, you fill out a questionnaire about your symptoms, medical history, and the medications you are interested in. The FTC’s lawsuit against Hims describes customers being automatically enrolled and billed for recurring prescriptions with “virtually no opportunity to review the provider’s recommended treatment.” That means you might sign up hoping for a one-time consultation and end up locked into a monthly subscription you did not fully understand. Researchers have found similar patterns across the industry, even for serious medications. A recent analysis of nearly fifty telehealth companies selling GLP-1 drugs, a class of injectable weight-loss medications that can have significant side effects and typically require a physical exam before starting treatment, found that less than a third actually required any real-time video or audio consultation with a physician. In some cases, prescriptions were approved within minutes of submitting an online form. For someone who genuinely needs medical advice, this can be dangerous. A doctor’s judgment involves more than checking a few boxes; it involves asking follow-up questions, reviewing your full health history, and considering interactions with other medications. When that human element is removed, the convenience comes at a cost. You might get the prescription you wanted, but you may not get the care you need.
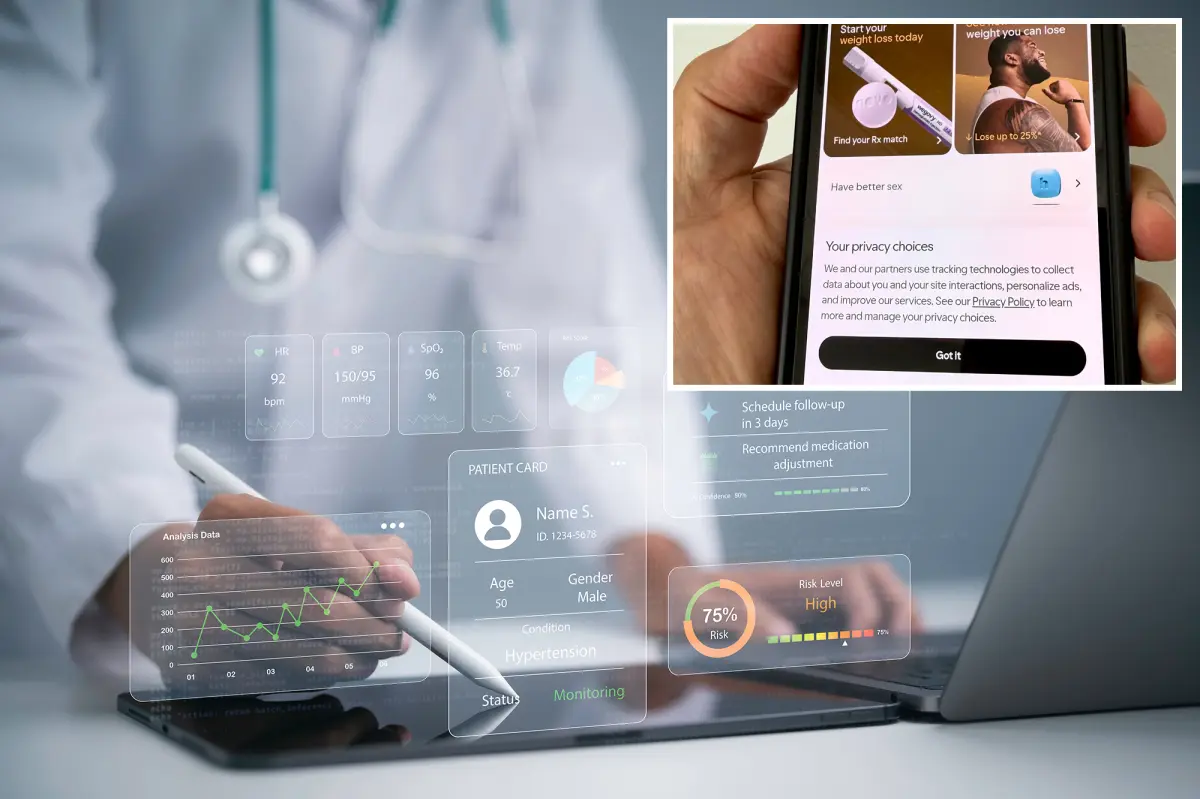
The privacy risks are just as concerning. Because HIPAA does not cover many telehealth platforms, companies have been able to collect and share health data in ways that would be illegal if done by a traditional medical office. The FTC has alleged that Hims told customers its platform was “100% online, private and secure,” but then shared sensitive information with Meta and other online platforms. GoodRx and BetterHelp faced similar accusations after allegedly sending user health data to advertisers for years. Privacy experts say this is not an edge case; it is a direct result of a legal framework that has not kept up with technology. Justin Brookman, Consumer Reports’ director of technology policy, notes that there is no clear federal law saying “Don’t do this,” only “a body of soft law and settled cases with the FTC that many companies probably aren’t even aware of.” Some states, including California, Connecticut, and Maryland, have passed their own online privacy laws with special protections for health information, but enforcement has been rare. Meanwhile, some telehealth sites explicitly state in their privacy policies that they have the right to sell data about users’ sex lives, mental health struggles, or other deeply personal matters. For someone who turns to these services precisely because they are too embarrassed or anxious to discuss those issues with a doctor in person, that revelation can feel like a profound betrayal. You came looking for privacy, and instead your most sensitive information becomes part of a digital marketing ecosystem.
So what can you do to protect yourself in this uncertain environment? Privacy experts recommend using ad blockers and private browsing modes, sometimes called “incognito” windows, when visiting telehealth websites. These tools can make it harder for companies to track your location, browsing history, and other identifying information. It is also wise to read the user agreement and privacy policy before signing up, even though these documents are often long and confusing. Crawford acknowledges that the burden on consumers is unfair. “The system we have now overly burdens consumers to do a ton of work in terms of understanding how each piece of technology collecting their personal data is going to handle it,” he said. “But even if you do all that work, you often have little agency.” The only truly surefire way to keep your information private is to decline the terms of service altogether, which usually means forgoing the telehealth visit entirely. That is not a realistic solution for people who need medication, especially those without easy access to a traditional doctor. Telehealth can be a valuable tool, and many people have received safe, effective care through these platforms. But the industry needs stronger rules, not just better marketing. Regulators must close the legal loopholes that allow health data to be treated like any other commodity, and consumers deserve transparent practices, clear consent, and real human connection when they seek medical help. Until then, the convenience of telehealth will remain shadowed by the very real risks of privacy violations, hidden subscriptions, and care that feels less like healthcare and more like a transaction.