

FBI Officially Names North Korea in $6 Billion Binance Cryptocurrency Heist
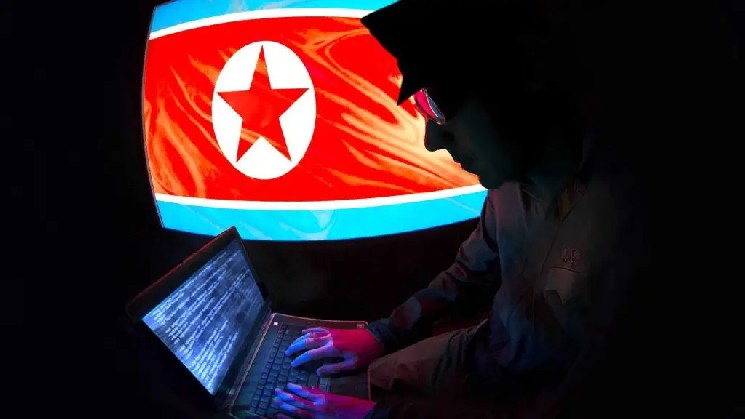
The Federal Bureau of Investigation has formally accused North Korea of masterminding the audacious theft of more than $6 billion in cryptocurrency from Binance, one of the largest digital asset platforms on the planet. In a statement made public on October 31, the FBI confirmed that the attack on October 29 — which sent shockwaves through global crypto markets and triggered fears across the industry — was carried out by a sophisticated state-linked hacking collective known as TraderTraitor. US officials said the perpetrators, a group with documented operational ties to the North Korean regime, moved with the kind of speed and precision that distinguishes state-sponsored operatives from ordinary cybercriminals, swiftly converting the stolen reserves into Ethereum and laying the groundwork for what could become a sprawling money-laundering operation. The announcement marked the first time American law enforcement has so directly and publicly pinned a heist of this magnitude on Pyongyang. It elevated what began as a security incident into a matter of international geopolitical concern. For an industry already navigating a punishing bear market, tightening regulation, and wavering public trust, the FBI’s verdict delivered a cold, clarifying truth: cryptocurrency has become a strategic target for rogue nations seeking to finance their ambitions beyond the reach of international sanctions. The agency didn’t stop with the accusation. In its statement, the FBI issued an urgent call to arms, urging cryptocurrency exchanges, blockchain infrastructure providers, and decentralized finance platforms to block any transaction traced to the hackers’ wallet addresses in an effort to prevent billions in stolen funds from vanishing beyond recovery.
That final piece of the FBI’s message may prove as consequential as the attribution itself. TraderTraitor is hardly a newcomer to the world of high-stakes digital crime. Over the years, researchers tracking North Korean cyber espionage have documented the group’s involvement in a series of brazen attacks targeting financial institutions, digital exchanges, and blockchain bridges across Asia and beyond. While the group has adopted multiple aliases and altered its methods to avoid detection, the fingerprints left behind in previous incidents have allowed intelligence agencies to build a detailed profile of its operational style. Within the security research community, TraderTraitor is widely regarded as an umbrella operation connected to the broader Lazarus Group — a notorious syndicate of state-backed hackers that has been blamed for a string of high-profile cybercrimes dating back more than a decade. In this latest attack, the group appears to have followed a now-familiar playbook: infiltrate the exchange’s security apparatus, identify the weakest access point, and exfiltrate funds in a matter of minutes rather than hours. The scale of the haul, however, was anything but routine. With more than $6 billion in crypto assets spirited away in a single operation, the Binance breach has eclipsed virtually every previous heist in the industry’s history, including some of the largest attacks ever publicly documented. Security experts say the audacity of this theft underscores a grim reality — North Korea’s cyber units have grown bolder, better funded, and considerably more effective as they refine their tactics with each successive operation. And the hundreds of millions of dollars in proceeds from past attacks, much of which has never been recovered, has likely bankrolled the sophisticated tooling and insider knowledge that made this week’s exploit possible.
The immediate aftermath of the attack unfolded with striking efficiency. Within hours of the breach, the stolen assets — a mixture of multiple cryptocurrencies held by the exchange — began moving across the blockchain in a carefully choreographed sequence of transactions. According to the FBI’s assessment, the attackers concentrated their efforts on converting the bulk of the haul into Ethereum, the second-largest cryptocurrency by market value. The decision was deliberate. Ethereum’s deep liquidity, wide range of decentralized applications, and interoperable ecosystem make it far easier to move large sums of money quickly without attracting the same degree of scrutiny that Bitcoin sometimes carries. More importantly, ethereum serves as the primary fuel powering the decentralized finance sector — the sprawling network of lending protocols, decentralized exchanges, and automated market makers that operate without traditional intermediaries. For TraderTraitor, that meant opportunity. By channeling the stolen funds into DeFi platforms, the hackers can swap assets, cross bridges to alternative blockchains, and tumble funds through a network of anonymous wallets with far less risk of seizure than they would face on regulated, custody-based exchanges. The FBI’s warning to DeFi platforms, therefore, carries weight precisely because these venues have historically been the hardest to police. Their permissionless nature, pseudonymous architecture, and global reach make them a haven for criminals seeking to launder proceeds — a challenge that governments and blockchain intelligence firms have been wrestling with for years. The agency’s message was unambiguous: if these platforms fail to cooperate in halting transactions tied to the flagged addresses, they risk becoming accomplices in one of the largest money-laundering operations ever witnessed in the digital asset space.
The FBI’s request for cooperation highlights a broader and increasingly urgent conversation about the limits of decentralized systems in an era of heightened national security concerns. In a traditional financial framework, frozen accounts and court-ordered asset seizures are well-trodden legal ground. In the borderless, pseudonymous world of crypto, such intervention is far more difficult — though not impossible. By publicly listing wallet addresses linked to the hackers, the Bureau has effectively pressed the industry into action. Major exchanges maintain transaction-monitoring tools designed to flag funds from known malicious actors, and compliance teams at leading platforms have a strong financial incentive to block suspicious transfers; failing to do so could expose them to sanctions enforcement, reputational damage, and regulatory penalties. Blockchain infrastructure providers, including node operators and custodians, are also being asked to scrutinize incoming transactions with heightened vigilance. For DeFi protocols, however, cooperation is more complicated. The very design of these platforms rejects centralized control, and many operate without a clear legal entity that can respond to federal demands. The tension between the ethos of decentralization and the practical demands of law enforcement sits at the core of this emerging crisis. It is one thing to champion the virtues of open financial networks; it is quite another when rogue states exploit that openness to launder proceeds from a heist that might fund ballistic missile programs. As the FBI intensifies its push to trace and recover the funds, the industry finds itself confronting a philosophical and operational reckoning: can decentralized finance remain true to its principles while becoming a reliable partner in the fight against state-sponsored crime?
Adding weight to the FBI’s conclusions, two of the blockchain intelligence world’s most respected independent analytics firms — TRM Labs and Chainalysis — have arrived at similar findings in their own post-incident investigations. Both companies maintain vast databases of blockchain transaction data, enriched over years of cooperation with law enforcement agencies and financial regulators around the world. Their attribution methodology typically involves tracing stolen funds across multiple hops, identifying clusters of wallets controlled by the same entity, and comparing behavioral signatures against known criminal infrastructure. In this case, both firms reportedly uncovered indicators pointing to North Korean-linked actors, reinforcing the government’s assessment with a layer of private-sector verification that is uniquely valuable in the murky world of on-chain investigations. The corroboration matters beyond mere consensus. When independent intelligence-gathering organizations, each using their own proprietary techniques, reach the same conclusion, the resulting credibility helps align international cooperation. Allies in Japan, South Korea, the European Union, and the United Kingdom — nations that have repeatedly clashed with North Korea over its missile tests and sanctions evasion — can be expected to treat the FBI’s warning with heightened seriousness. Shared intelligence about the flagged wallet addresses could quickly ripple across global financial watchdogs, triggering coordinated enforcement actions designed to choke off the hackers’ ability to spend their stolen riches. Yet even as the investigators display formidable skill at tracking digital footprints, they face an opponent that grows more adaptive by the month. The recovery rate for North Korean crypto thefts has historically been low, and the odds of seizing all $6 billion back are slim. What remains realistic, experts suggest, is disrupting the laundering chain enough to render a substantial portion of the loot unreachable — and, just as importantly, sending a message to Pyongyang that the cost of these operations continues to rise.
The broader impact of the Binance attack extends well beyond the balance sheets of a single exchange, arriving at a moment when the crypto market is already under intense strain. Bitcoin has suffered renewed selling pressure in recent days, and market sentiment, while never far from volatile, has turned increasingly cautious. Against this backdrop, financial analysts have begun reassessing entry points for those looking to buy the dip. Among them, well-known crypto trader Michaël van de Poppe has publicly outlined the level at which he intends to accumulate bitcoin if the decline continues — a signal to his substantial following that further downside may be on the table before a meaningful recovery takes shape. The intersection of these market dynamics with the Binance news paints a stark picture for the industry: headlines about state-sponsored theft have a visceral effect on investors, reinforcing anxiety about security, regulatory crackdowns, and the long-term viability of centralized exchanges. In Washington, lawmakers have seized on the attack as another justification for stricter oversight of digital assets, and the debate over how to balance innovation with national security is likely to intensify in the coming months. For the countless businesses, developers, and everyday users who have staked their futures on cryptocurrency, the path forward demands a maturity the industry has not always displayed. Security cannot be an afterthought; it must be the foundation upon which trust is rebuilt. In the stark light of the FBI’s announcement, one truth stands out above the rest: cryptocurrency has entered a new era in which its promise of freedom and innovation exists in permanent tension with the very real threats posed by adversaries determined to exploit every weakness. The industry’s response to this challenge will define not only its survival, but its credibility as a legitimate pillar of global finance.